Protect. Comply.
Thrive.
Cybersecurity, compliance, and risk advisory that keeps regulated organizations resilient as threats change.
RB Advisory provides CMMC consulting and advisory services to organizations across the Defense Industrial Base.
Protecting Businesses and Governments
at Every Layer
Cybersecurity, risk management, compliance, and cyber-physical security for organizations that can't afford to get security wrong.
We equip you with current practice and proven methodology, so a cyber attack never becomes a business event.
See our security services
We find the risks hiding in your environment and put safeguards around them before they reach legal, operational, and financial well-being.
How we assess risk
We assess and reduce your cyber risk, then build the compliance program your sector requires to protect the integrity, confidentiality, and availability of information.
Explore compliance programs
We secure the systems that run your physical operations. When industrial controls, connected devices, and building systems share a network, a cyber incident becomes a safety and downtime problem.
Secure your operations
Your Trusted
Cybersecurity Experts
Helping businesses stay secure and compliant as threats change. Across five regulated industries, we deliver measurable results, not just recommendations.
Get in TouchWe Don’t Just Identify Risk.
We Help You Make Better Decisions.
Most cybersecurity firms deliver assessments. RB Advisory delivers decision intelligence. Through proprietary platforms, executive advisory, and hands-on implementation, we help organizations understand risk, prioritize action, and achieve measurable business outcomes.
RBA brings enterprise-scale experience to complex, regulated environments. Our work is grounded in measurable performance and executive-ready visibility.
Major Industries Served
Specialized cybersecurity, risk, and compliance for the regulated sectors where the stakes are highest.
Service Pillars
Across Industries
A command-center view of our practice. Pick an industry to light up its pillars and compliance framework, open a pillar to see its tools, or select a focus area to see the services it spans.
Prefer a list? The same sectors, pillars and focus areas as text
Sectors we serve
| Sector | Framework | What it covers |
|---|---|---|
| Healthcare | HIPAA / HITRUST | Providers and health systems protecting patient data (PHI) and continuity of care. |
| Defense Industrial Base | NIST 800-171 · CMMC | Defense contractors safeguarding controlled unclassified information (CUI). |
| Financial Services | Federal/State Regs · PCI | Banks, credit unions, and fintechs meeting examiner and payment requirements. |
| Government | CJIS 6.0 | Agencies protecting citizen data and critical public services. |
| Higher Education | FERPA · HIPAA · GLBA | Universities and colleges protecting student records, research, and campus systems. |
| Retail | PCI | Retailers protecting payment and customer data across stores and e-commerce. |
| Technology Companies | ISO 27001 · SOC | Tech firms proving security and trust to their own customers. |
| Restaurant | PCI | Restaurants protecting payment systems and guest data across locations. |
Service pillars
Cybersecurity
Protecting systems, networks, and data — from risk assessments and penetration testing to vCISO™ leadership.
11 tools & services: Cyber Risk Assessments, Gap Analysis, Vulnerability Management, Penetration Testing, Threat Intelligence, Cyber Security Strategy Plan, M&A Due Diligence, Virtual CISO (vCISO™), Virtual ISSO (vISSO), CJIS 6.0, Risk Management Framework.
Compliance
Meeting the frameworks your sector answers to — HIPAA, HITRUST, CMMC, PCI, ISO 27001, SOC, and more.
11 tools & services: Governance, Risk & Compliance (GRC), Privacy Consultations & Safeguards, Federal & State Regulations, PCI, HIPAA / HITRUST, NIST 800-171 / CMMC, ISO 27001 & ISO Family, SOC Family, Education Awareness Training, Policies & Procedures, NIST CSF 2.0.
Risk Management
Finding and managing operational and third-party risk — audits, incident response planning, and cyber insurance readiness.
7 tools & services: Cyber Risk Management Plans, IT Security Audits, Incident Response Plan, Third Party Vendor Risk Management, Cloud Infrastructure & Management, Change Management, Cyber Liability Insurance.
Data Management
Turning data into decisions — analytics, business intelligence, and governance across Power BI and Tableau.
14 tools & services: Power BI, Tableau, Business Impact Assessment, Data Strategy, Data Integration, Performance Management, Monitoring & Evaluation, Predictive Analytics, Data Quality Assurance, Needs Analysis Assessment, RPA Strategy & Roadmap, Center of Excellence, Privacy Impact Assessment, Fractional CDIO (vCDIO).
Technology Solutions
Modernizing and building the technology that runs the business — from digital transformation to staff augmentation.
8 tools & services: Digital Transformation, Solutions Development, Solutions Architecture, Staff Augmentations, Reliability Engineering, Tools Assessment, Power BI, Tableau.
Physical Security
Protecting people, facilities, and assets — executive protection, access control, and cyber-physical strategy.
10 tools & services: Executive Protection Program, Access & Controls Management, Asset Discovery & Risk Assessment, Cyber-Physical Security Strategy, Program Design & Implementation, Technology Assessment, Security Training, Vendor Assessment, Data Closet Assessment, Fractional Global Safety & Security Officer (vGSSO).
Cyber-Physical
Securing the systems that run physical operations — OT, ICS, IoT, and building systems where a cyber incident becomes a safety or downtime problem.
11 tools & services: Cyber-Physical Risk Framework, OT & ICS Security Assessment, IT / OT / IoT Convergence Strategy, Continuous Asset Discovery, Zero Trust Architecture, Supply Chain & Vendor Compromise Review, Cyber-Physical Incident Response Exercises, Privileged Access Management, OT & ICS Network Monitoring, Smart Building & Access System Security, Executive Cyber Resilience Program.
Focus areas
- Risk Assessment — Measuring where you are exposed and what to fix first. Delivered through: Cybersecurity (11), Risk Management (6), Compliance (4), Data Management (9), Technology Solutions (7), Physical Security (7), Cyber-Physical (6).
- Governance — The policies, oversight, and accountability that run security. Delivered through: Cybersecurity (9), Risk Management (6), Compliance (10), Data Management (11), Technology Solutions (8), Physical Security (6), Cyber-Physical (4).
- Security Organization — Structuring the people and roles that own security. Delivered through: Cybersecurity (10), Risk Management (6), Compliance (10), Data Management (15), Technology Solutions (7), Physical Security (5), Cyber-Physical (4).
- Security Tools — Selecting and tuning the tools that detect and defend. Delivered through: Cybersecurity (9), Risk Management (4), Compliance (10), Data Management (11), Technology Solutions (7), Physical Security (9), Cyber-Physical (5).
- Third Party Risk — Managing the risk your vendors and partners introduce. Delivered through: Cybersecurity (9), Risk Management (5), Compliance (10), Data Management (12), Technology Solutions (6), Physical Security (10), Cyber-Physical (4).
- Threat Management — Finding and acting on active threats and intelligence. Delivered through: Cybersecurity (7), Risk Management (6), Compliance (11), Data Management (12), Technology Solutions (7), Physical Security (9), Cyber-Physical (5).
- Incident Response — Preparing for, containing, and recovering from incidents. Delivered through: Cybersecurity (3), Risk Management (3), Compliance (9), Data Management (10), Technology Solutions (7), Physical Security (8), Cyber-Physical (4).
- Regulatory Compliance — Meeting the rules and frameworks your sector requires. Delivered through: Cybersecurity (2), Risk Management (1), Compliance (9), Data Management (6), Technology Solutions (4), Physical Security (8), Cyber-Physical (4).
- Cyber Liability Insurance — Qualifying for coverage and meeting insurer requirements. Delivered through: Cybersecurity (6), Risk Management (6), Compliance (9), Data Management (7), Technology Solutions (6), Physical Security (6), Cyber-Physical (4).
- Data Analytics — Turning raw data into insight and reporting. Delivered through: Cybersecurity (6), Risk Management (3), Compliance (8), Data Management (9), Technology Solutions (7), Physical Security (9), Cyber-Physical (3).
- AI — Applying AI safely and putting it to work. Delivered through: Cybersecurity (11), Risk Management (6), Compliance (10), Data Management (12), Technology Solutions (8), Physical Security (10), Cyber-Physical (5).
- Business Intelligence — Dashboards and reporting that inform decisions. Delivered through: Cybersecurity (9), Risk Management (6), Compliance (10), Data Management (10), Technology Solutions (6), Physical Security (8), Cyber-Physical (3).
- Data Governance — Controlling how data is classified, stored, and accessed. Delivered through: Cybersecurity (8), Risk Management (6), Compliance (10), Data Management (8), Technology Solutions (5), Physical Security (10), Cyber-Physical (4).
- Robotics Process Automation — Automating repetitive processes to save time and cost. Delivered through: Cybersecurity (8), Risk Management (6), Compliance (10), Data Management (10), Technology Solutions (8), Physical Security (7), Cyber-Physical (4).
- Program Management — Running security initiatives as coordinated programs. Delivered through: Cybersecurity (11), Risk Management (6), Compliance (10), Data Management (15), Technology Solutions (8), Physical Security (10), Cyber-Physical (4).
- Process Improvements — Streamlining how the work actually gets done. Delivered through: Cybersecurity (11), Risk Management (6), Compliance (10), Data Management (16), Technology Solutions (8), Physical Security (10), Cyber-Physical (5).
Ahead of
Emerging Threats
Expert analysis, regulatory updates, and actionable guidance from the RB Advisory team.
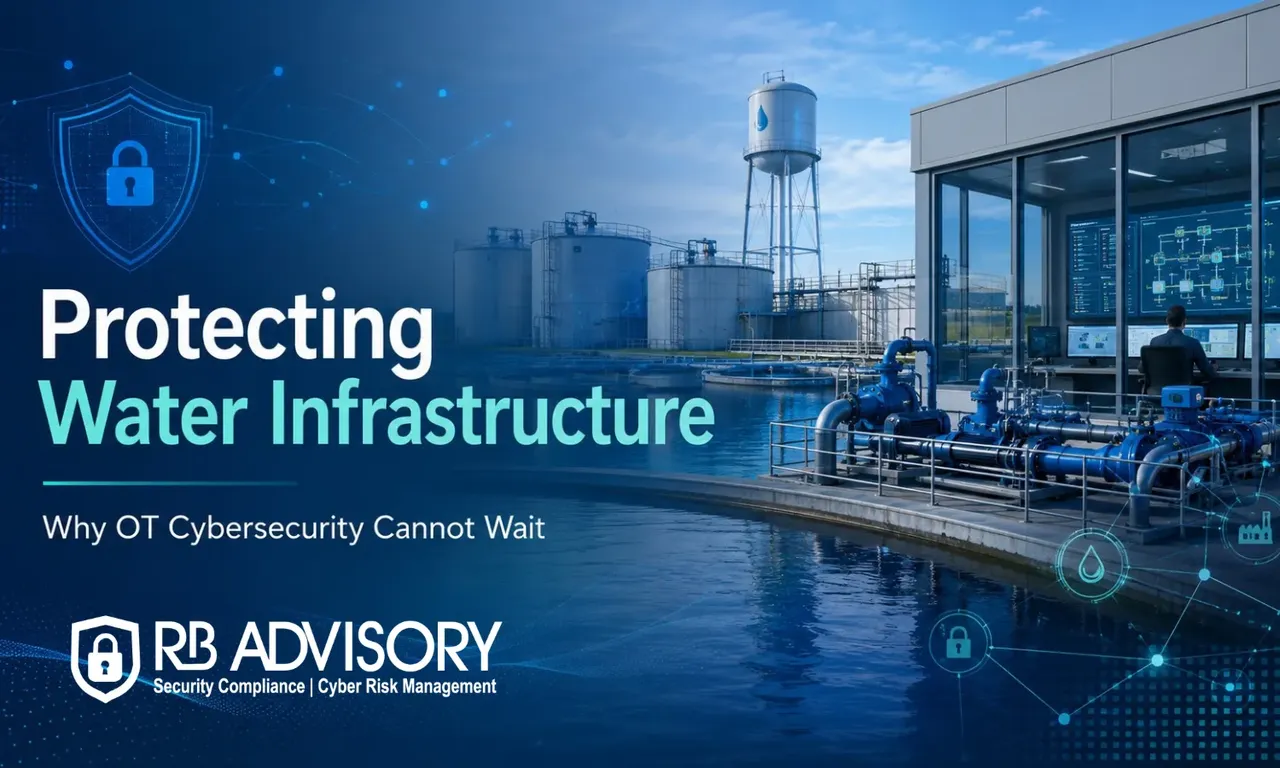 Cybersecurity
Operational technology connected to the public internet can turn a cyber intrusion into a physical disruption. What recent utility incidents mean for critical infrastructure.
 Cybersecurity
 still feels like a technical issue handled somewhere inside the IT department. That framing is exactly where risk hides.
 Compliance
Passing the audit and being protected are two different things. Where regulatory certification ends and real security begins.
 AI
AI is no longer a lab experiment. It is a production-grade capability reshaping how organizations operate, and how they get attacked.
Trusted by Organizations
That Demand Results
Hear from the organizations we've helped protect, transform, and strengthen.
The entire process from start to finish has been exceptionally easy to go through, while being extremely thorough. The documentation outlined exactly where we lacked and what we could do to remediate the issues. They worked with us on every step and worked around our schedule. We highly recommend their services.
RBA took the time to understand my business needs, initiatives, and clients in order to properly provide the services and support we needed — creating a program that was customized, with actionable and real-life solutions.
RB Advisory performed network penetration and phishing testing for us. Their team was communicative and professional. After the test results, they offered solutions to help minimize found risks and to assist with phishing training. We will definitely be using annually for testing!
Working with RB Advisory has been a pleasure. We have engaged them to provide comprehensive cybersecurity systems across our business networks. Building a fully compliant, long-term solution is critical to our business, and we are thankful to partner with such an experienced firm.
Secure Your Organization.
Start With a Conversation.
Free 30-minute strategy session with a cybersecurity expert. We'll assess your current posture and outline a clear path forward.
Book Your Consultation